Retainer capacity is full until mid-2027.Fixed-scope projects available on request.
The security owner your company needs,
at the size you are.
European SMEs get one senior practitioner running security month to month: understanding the gaps, building the right controls, producing the evidence customers ask for, and handling NIS2 or ISO 27001 where they genuinely apply.
Every enquiry gets a reply, with a recommendation for your situation - whether the work is a fit or not.
SteadySec
Led by Petr Pospíšil, vCISO & Security Architect
Based in Prague. Remote-first across Europe.
The Problem
The hard part is
knowing where to start.
- A customer questionnaire arrives, and no one can answer it.
- Some security exists, but nobody knows where the real gaps are.
- Tools get bought to suit the vendor's roadmap.
That is chaos.
The fix is one senior owner for the whole picture.
One retained partner to assess, prioritise, implement, and prove, month after month.
The Core Engagement
Retained Security Partner
Advisor, architect, and engineer on demand
One engagement that moves security forward month by month, at a pace your business can absorb. Frameworks fit around that work as your situation calls for them:
- NIS2 where it reaches you directly or through a customer auditing its suppliers
- ISO 27001 where a buyer or an investor wants the certificate
- CIS Critical Security Controls where a solid baseline is the goal
The free security path calculator points to the one that fits.
Final accountability for security decisions stays with your management.
What the retainer covers
- Security ownership
- Risk management
- Architecture & controls
- Compliance & assurance
- Supplier & vendor decisions
- Board reporting
The first 90 days
What actually changes
- Ownership in place Security decisions have a name on them
- Risks ranked Ordered by business impact
- Evidence pack started Questionnaires answerable from one place
- Roadmap agreed Costed, sequenced, owned by management
- First gaps closed The highest-risk ones first
Where to Start
Two ways in
Book a discovery call
A pentest with a deadline, an audit already booked, a questionnaire on your desk. Talk it through in 30 minutes and you get a straight answer on fit, effort, and when it could start.
Book a discovery callRun the Discovery Calculator
Two free calculators, no sign-up: one maps your situation to the right security path, the other says where the Cyber Resilience Act leaves your product. Both send the result from the last screen.
Open the Discovery CalculatorProject Work
Fixed-scope projects, bought on their own
One-time projects with a fixed scope and a fixed price.
Scoped testing of your web application or API, with findings you can act on.
View scope & pricingAI assistants and agents tested for what an attacker can make them do.
View scope & pricingA configuration and privilege review of the paths ransomware uses to spread.
View scope & pricingA realistic campaign that measures how your people actually respond.
View scope & pricingInteractive sessions that build judgement, for executives, boards, and technical teams.
Explore workshopsA guided incident scenario that tests your decisions before a crisis does.
Explore exercisesAny project can lead into the retainer later. ISO 27001, NIS2, and CIS Controls work always runs through the retainer - that work only holds up if someone stays with it.
Client proof
What clients say
Private-sector clients who agreed to be named. Each reference was published by the client, and it is quoted here in full.
 VisstoTwo penetration testing projects
Petr worked with us on two penetration testing projects. The collaboration was professional and free of friction, and the results were delivered on time and to a high standard. I value his expert approach, his communication, and his ability to identify risks and to propose practical measures. I am glad to recommend his services to anyone looking for a reliable cybersecurity expert.
Translated from Czech
S Petrem jsme spolupracovali na dvou projektech penetračního testování. Spolupráce byla profesionální, bezproblémová a výsledky byly dodány včas a ve vysoké kvalitě. Oceňuji jeho odborný přístup, komunikaci a schopnost identifikovat rizika i navrhnout praktická opatření. Rád doporučím jeho služby každému, kdo hledá spolehlivého experta na kybernetickou bezpečnost.
 KontextaSecurity review and implementation plan
I cannot praise the work with Petr enough. It was fast, clear and very helpful. We were given a clear plan of what to implement, and within a very short time frame. It is obvious that he knows the field well and knows what he is talking about. I recommend him warmly.
Translated from Czech
Spolupráci s Petrem si nemohu vynachválit. Byla, rychlá, jasná a velmi nápomocná. Dostali jsme jasný plán, co implementovat a to během velmi krátkém časovém horizontu. Jde vidět, že se v oboru velmi orientuje a ví, o čem mluví. Vřele doporučuju.
Published on the Na volné noze profile, where they can be read at source. Other clients are not listed: without written approval to publish, a name stays off this page.
Leadership
Who does the work
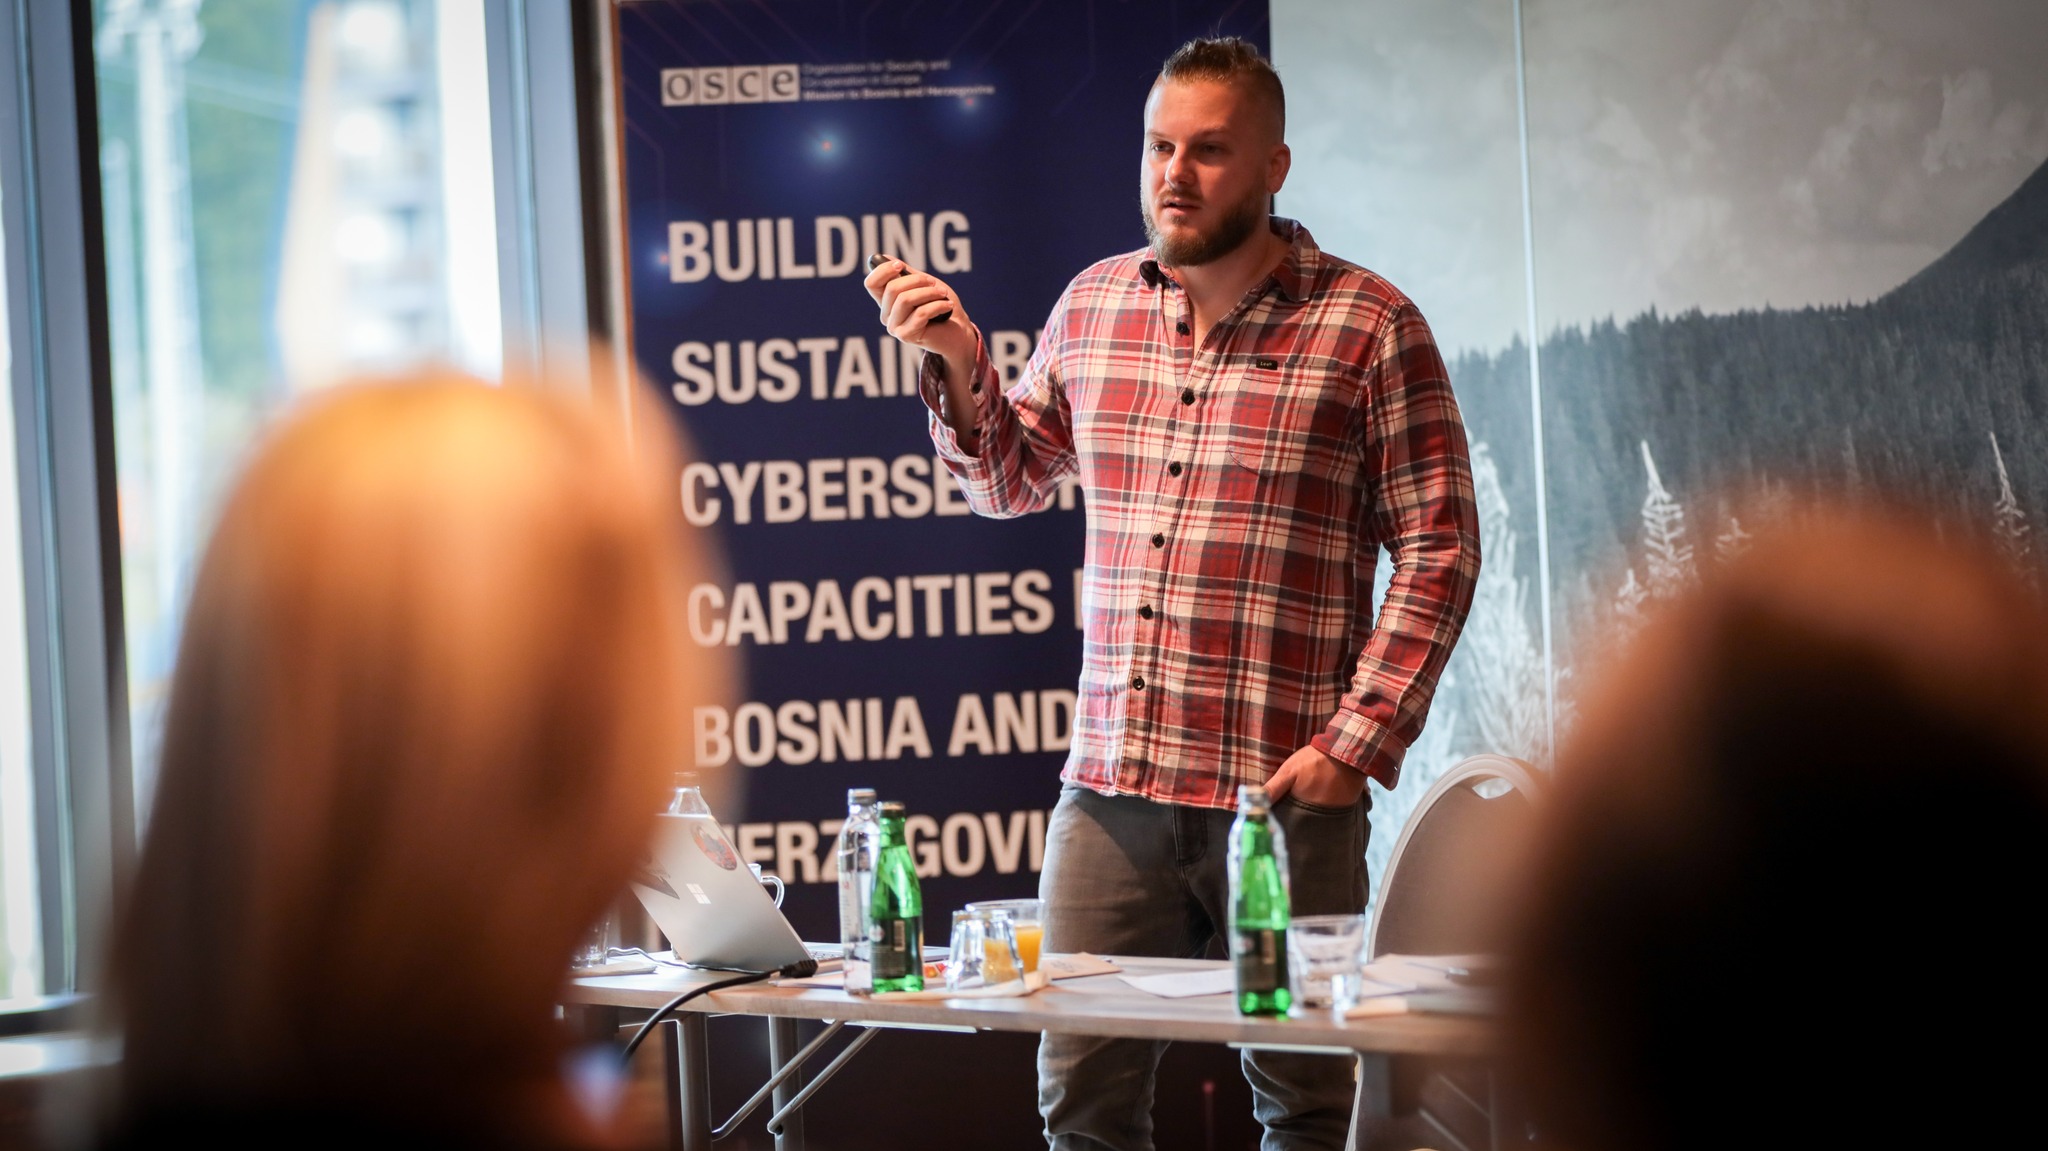
Petr Pospíšil
vCISO & Security Architect
Attack. Defend. Architect. Advise.
Security must be practical to deploy, strong enough to pass client audits, and cost-effective for a business to maintain.
Certifications
- CISSP · ISC2
- ISO 27001 Lead Auditor · IRCA certified course
- GCTI · GIAC
- GCDA · GIAC
- CRTP · Altered Security
- SecurityX · CompTIA
Listed, vetted, and contracted by institutions
- EU CyberNet Roster of EU experts
- UNDP Vetted expert roster, capacity-building delivery
- EEAS Cybersecurity expert, EU CSDP mission
- OSCE Capacity-building programme delivery
These are the rosters and mandates that put Petr in front of European and international institutions, each with its own selection process before an expert gets near the work.
Experience
- 01 Ethical hacker / Penetration tester Testing defences by attacking them
- 02 Threat hunter / L2-L3 Security Analyst Hunting intruders, investigating incidents
- 03 Cyberdefense and Operations Manager Running defence for a global retailer
- 04 Independent security consultant Advising European organisations on security, architecture and compliance
Methodology
Management owns the business risk. The job is to make it visible and help you decide what to accept, transfer, or fix first. Plan, Do, Check, Act: documented process over quick fixes.
Senior capabilitiesGet In Touch
Ready to start?
If a customer questionnaire, an audit, or a NIS2 scope question is creating pressure, let's turn it into an assessment, a roadmap, and a monthly rhythm.